Crypto news report · source clearly identified
Three-Year-Old Radix Engine Bug Leads to $1.3 Million Theft and 10-Day Network Halt
A routine code refactor introduced a vault flaw that enabled a roughly $1.3 million theft and forced validators to halt the Radix blockchain for over ten days.
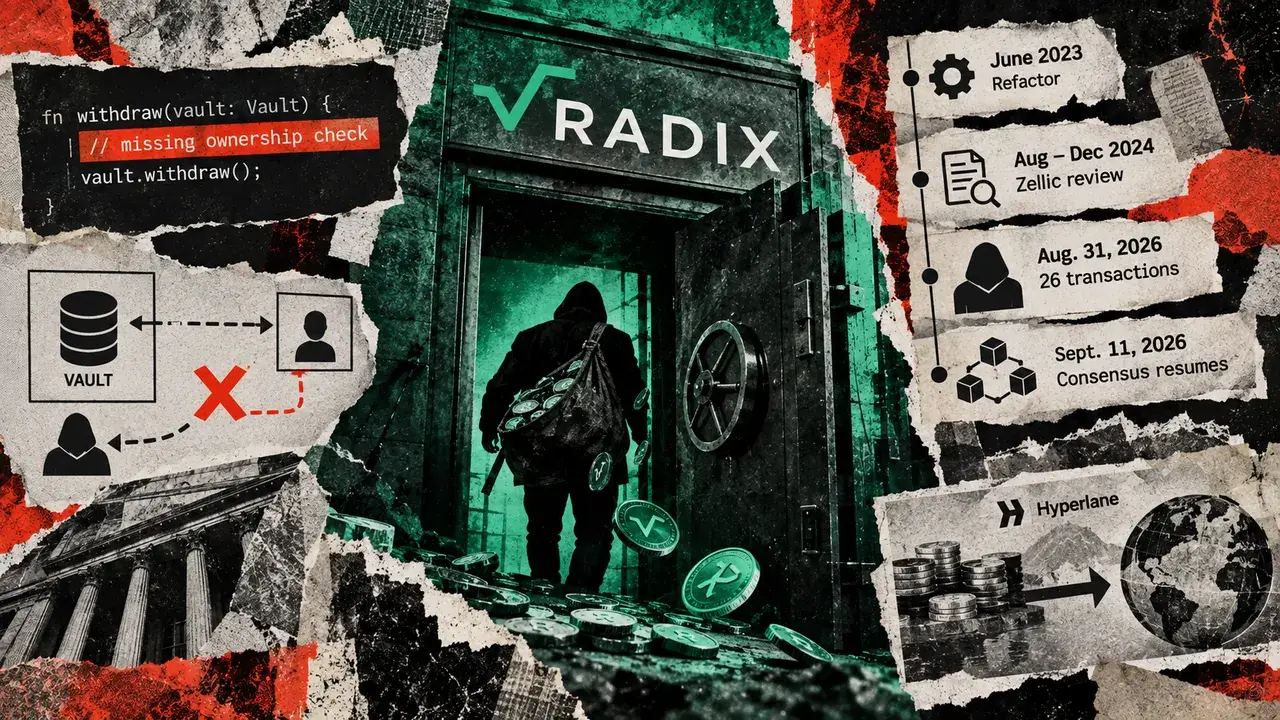
A recent incident on the Radix network exposed a three‑year‑old vulnerability in the Radix Engine, the core software that processes transactions and enforces asset ownership. The flaw, introduced during a June 2023 code cleanup, was exploited on August 31, 2026, resulting in the theft of approximately $1.26 million and a network shutdown that lasted more than ten days.
How the Exploit Unfolded
The vulnerability altered the way the engine handled vault references. By passing a reference to another user’s vault into specially crafted smart‑contract code, the engine allowed ordinary withdrawal functions to execute without proper ownership checks. This granted the attacker access to assets held in user accounts, applications, and liquidity pools without requiring the owners’ signatures.
Stolen Assets
- 458,915 USDC
- 72,420 USDT
- 61.08 ETH
- 6.35 wrapped Bitcoin (WBTC)
- 536.16 SOL
- 32.91 BNB
- 13,000 XRD (used for transaction fees)
The assets, valued at roughly $1.26 million based on August 31 market prices, were moved through the Hyperlane bridge to Ethereum, BNB Chain, and Solana before being sold for ETH.
Network Response and Halt
After confirming that the flaw resided in the execution layer rather than a single application, Radix validators deliberately took sufficient stake offline to prevent consensus, halting transaction finalization. The pause lasted until September 11, when a protocol fix—adding checks to block restricted vault references from ordinary withdrawals—was deployed.
Audit Miss and Future Measures
The defect survived an independent security audit conducted by Zellic in 2024, which did not detect the authorization issue. In response, the Radix Foundation announced several remedial steps:
- Implementation of additional regression tests for authorization logic.
- Strengthening of the security review process, including consideration of AI‑assisted code‑analysis tools.
- Formalization of emergency procedures for validators to suspend network liveness when critical bugs are discovered.
Secondary Economic Impact
Beyond the direct theft, the exploit caused secondary losses in liquidity pools. The removal of bridged assets distorted pool prices, enabling another account to extract millions of XRD from affected pools, illustrating how execution‑layer failures can generate ongoing economic damage.
Source & attribution
News Source
- Publisher
- CryptoSlate
- Original date
- September 18, 2026, 5:50 PM
- Original headline
- 3-year-old bug triggers $1.3 million drain and forces 10-day blockchain halt