Crypto news report · source clearly identified
Coinbase Traces $1.1 Million Crypto Trail Behind AI Phishing Service EvilTokens
EvilTokens abused Microsoft’s real device-login flow to authorize attacker sessions, then used AI to identify payment authorities inside captured mailboxes.
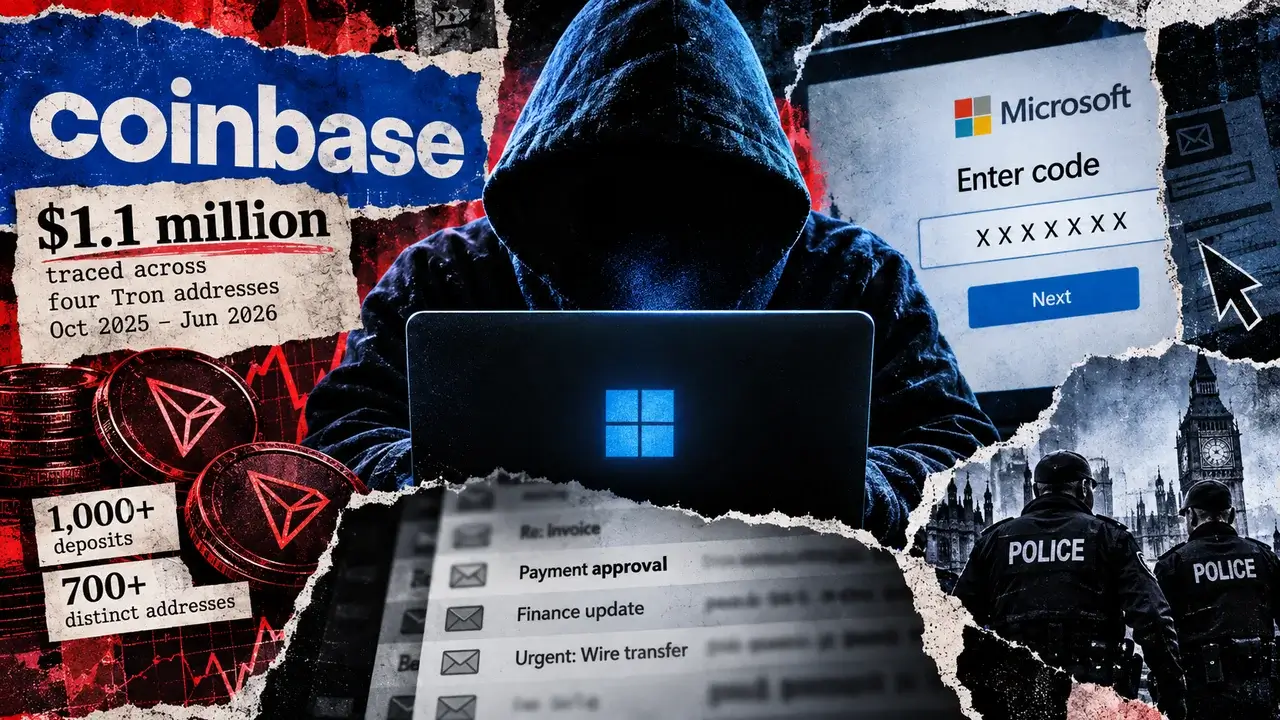
Microsoft and Coinbase collaborated to dismantle EvilTokens, an AI‑driven phishing service that compromised more than 12,000 inboxes worldwide. The operation targeted a broad range of sectors, including financial services, real estate, healthcare and construction.
How EvilTokens Operated
The service packaged the business‑email‑compromise process into a subscription sold via Telegram. Customers paid a $1,500 initiation fee and a $500 recurring subscription for tools that combined account compromise, mailbox access, reconnaissance and AI‑assisted fraud preparation.
Attackers leveraged Microsoft’s device‑code authentication flow, a legitimate sign‑in method for devices such as smart TVs. Phishing emails containing the generated code prompted victims to approve the session on Microsoft’s website, granting attackers an authenticated foothold inside the mailbox.
AI‑Powered Reconnaissance
Once inside, EvilTokens used AI to translate, summarize and analyze email content, identifying reporting lines, trusted contacts, pending invoices and wire‑transfer discussions. Preset prompts could pinpoint an organization’s “money movers,” enabling attackers to craft targeted impersonation campaigns with minimal manual effort.
Crypto Payments Reveal the Revenue Trail
Coinbase’s Global Intelligence team traced approximately $1.1 million in revenue paid to EvilTokens across four Tron addresses between October 2025 and June 2026. The analysis uncovered more than 1,000 deposits from over 700 distinct addresses and mapped the flow of funds to eventual cash‑out destinations.
Coinbase combined transaction data with merchant records, device information and open‑source intelligence to attribute the platform to its alleged operators and referred the findings to London’s Metropolitan Police. The exchange also identified EvilTokens purchasers on its platform and reported them to law enforcement.
Law Enforcement Action
Microsoft and its partners seized 50 websites used by EvilTokens and disabled over 150 related domains. UK police arrested two suspects on September 11, later releasing them on conditional bail.
Future Risks and Recommendations
EvilTokens’ operator indicated plans to extend the toolkit to Gmail and Okta accounts, suggesting the model could proliferate across other identity platforms. Microsoft advises organizations to block device‑code authentication where unnecessary, restrict it where required, revoke refresh tokens for compromised accounts, and consider temporary account disabling to cut off lingering access tokens.
Source & attribution
News Source
- Publisher
- CryptoSlate
- Original date
- September 23, 2026, 10:20 AM
- Original headline
- Coinbase traced $1.1 million crypto trail behind AI phishing service EvilTokens