Crypto news report · source clearly identified
GalaChain exploit used 55‑day old failed signatures to drain $3 million in GALA
A flaw in GalaChain’s signature verification and replay protection allowed an attacker to reuse signatures from failed transactions spanning 55 days, draining roughly 2 billion GALA and other tokens from nine wallets.
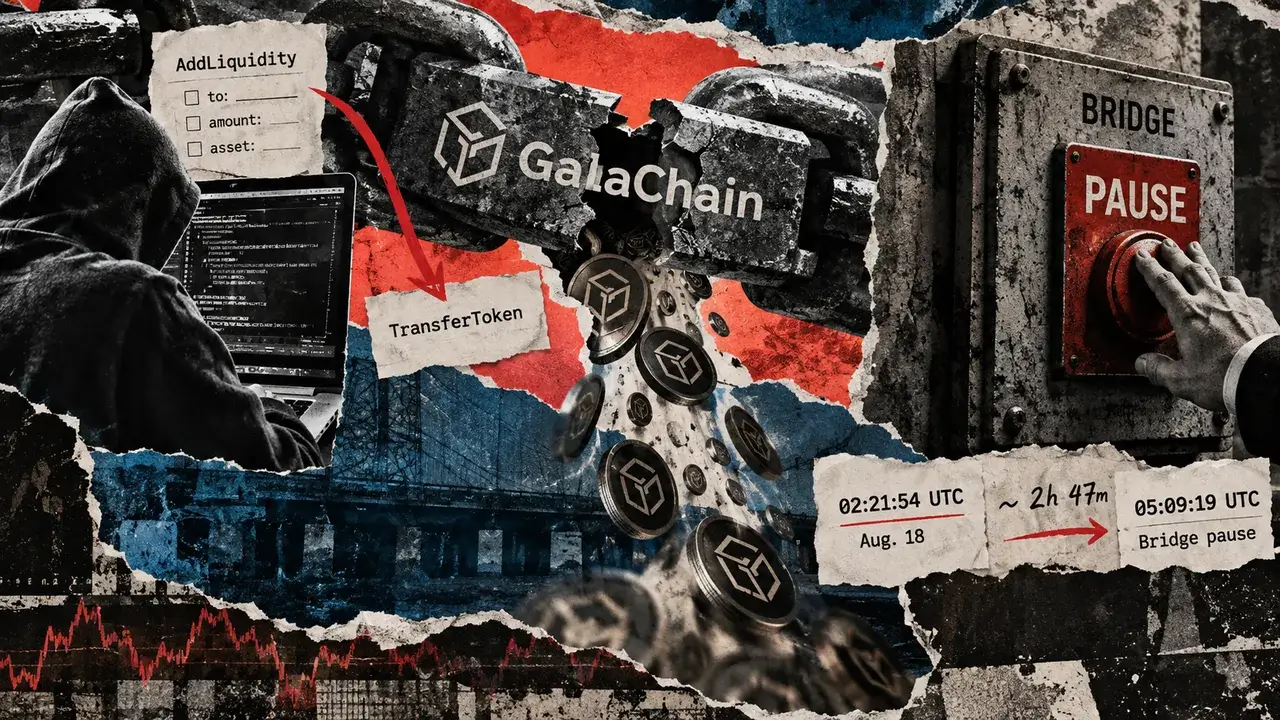
On August 18, an attacker leveraged historical signatures from failed GalaChain transactions to move about 2 billion GALA (approximately $3 million) and several other tokens out of nine wallets.
How the attack worked
The attacker collected 74 signatures from transactions that had failed over the previous 55 days. Because GalaChain’s EIP‑712 verifier accepted type definitions supplied by the caller, a signature created for one operation could be replayed on a different method, allowing the attacker to submit a TransferToken call that was authorized by a signature originally intended for an AddLiquidity operation.
In addition, GalaChain’s replay protection used a unique transaction key that was reset when a transaction failed, leaving the signed payload publicly visible while the key remained reusable. This turned unsuccessful requests into valid permissions without needing to compromise private keys.
Attack execution
- 59 account‑token pairs were targeted; 56 were drained on the first attempt.
- The four largest GALA balances were emptied in descending order within 18 seconds.
- 1,066 submissions were recorded, with a median interval of 4.5 seconds; 73.9 % arrived exactly one block apart.
Response and mitigation
GalaChain paused its bridge at 05:09:19 UTC, roughly two hours and 47 minutes after the first unauthorized transfer, and began revoking the attacker’s roles shortly thereafter. Post‑mortem patches include:
- Signature verification now derives type information from the called method rather than trusting caller‑supplied definitions.
- Signatures are bound to specific contracts, channels, and methods, with expiration timestamps.
- Replay keys persist even after a failed operation, preventing reuse of failed payloads.
- Per‑identity rate limits, behavioral monitoring for high‑value accounts, and additional review for large bridge withdrawals.
Broader implications
The incident highlights a “machine‑speed” defense problem for blockchain operators: once an attacker automates valid‑looking transactions, human‑triggered emergency controls may be too slow. It also underscores the need for audits that examine the interaction between signature verification, replay protection, and transaction execution, rather than testing each component in isolation.
GalaChain has filed a complaint with the FBI’s Internet Crime Complaint Center and issued preservation requests to platforms across four chains to track the stolen assets.
Source & attribution
News Source
- Publisher
- CryptoSlate
- Original date
- September 17, 2026, 11:30 AM
- Original headline
- Hacker turned 55 days of failed transactions into a $3 million master key that drained GalaChain wallets