Altcoins
Neutral
Hackers hijack Microsoft X account to promote fake Clippy crypto token
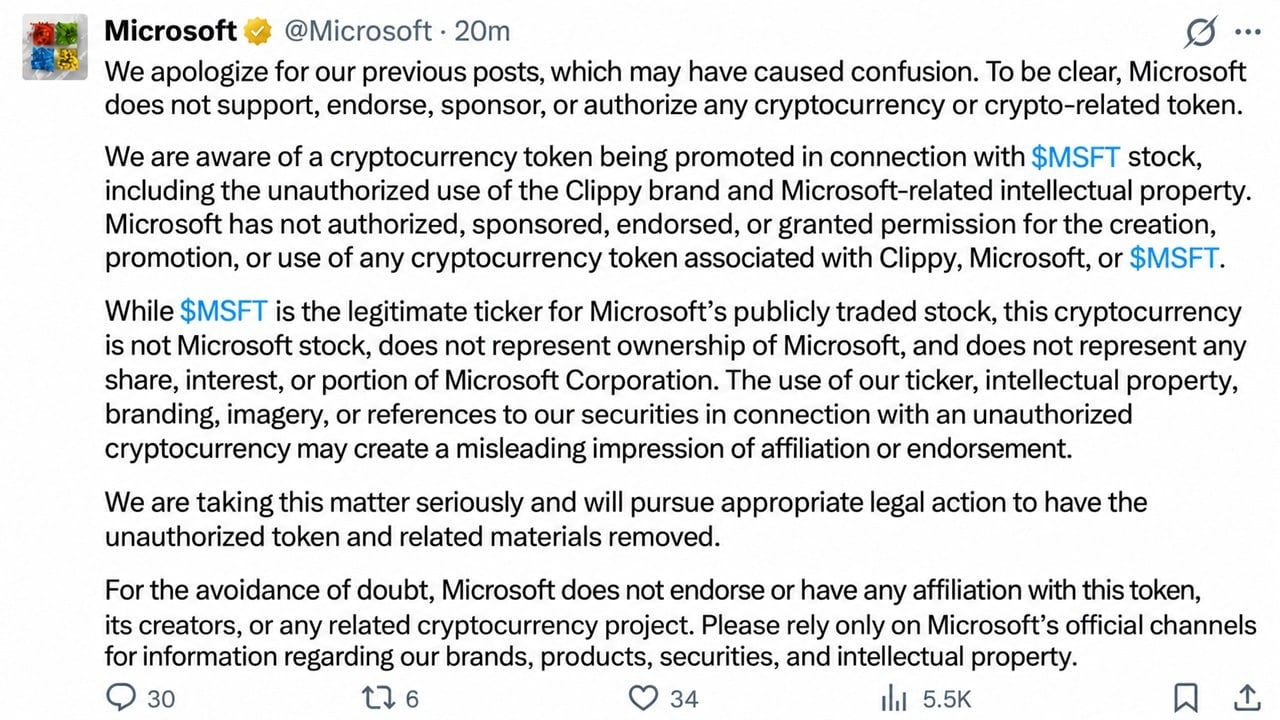 Image: Bitcoin.com News
On October 2 2026, attackers hijacked Microsoft's official X account for roughly 30 minutes. They changed the account's profile picture to Clippy, interacted with an impersonator account, and posted promotions for the fraudulent $Clippy token. Microsoft regained control of the account, removed the misleading posts, and issued a formal denial of any association with the token or $MSFT. The impersonator account was suspended, and there was no immediate impact on Microsoft shares or digital assets.
Key points
- The hijacked account was used to promote the fraudulent unaffiliated $Clippy crypto token.
- Microsoft regained control of the account, removed the posts and denied any link to the token.
- This is the second time a Microsoft X account has been hijacked to push a fake crypto token, after a 2024 incident.
Why it matters
The incident highlights the risk of scammers using corporate social accounts to promote fraudulent crypto tokens. Repeat hijackings of Microsoft accounts suggest attackers see large corporate profiles as reliable targets for these schemes.
What's unclear
Why Microsoft deleted its initial apology tweet following the account hijack
Whether claims that $Clippy token liquidity pools are backed by Microsoft shares are accurate
Sources · 2 publishers
Bitcoin.com News
Tier 2
Microsoft’s X Account Hijacked to Promote Clippy Meme Coin
Coverage timeline
- First reported by Crypto Briefing
- Confirmed by Bitcoin.com News
- CryptoVideos brief published
How this brief was made. Our system found this event in 2 independent publications, summarised two complete reports with AI and checked every number above against the source text. Sources are linked in full. Not financial advice. Report an error