Hacks & Security
Bearish
PHP flaws scored 9.2 patched as BitGo and CZ issue warnings
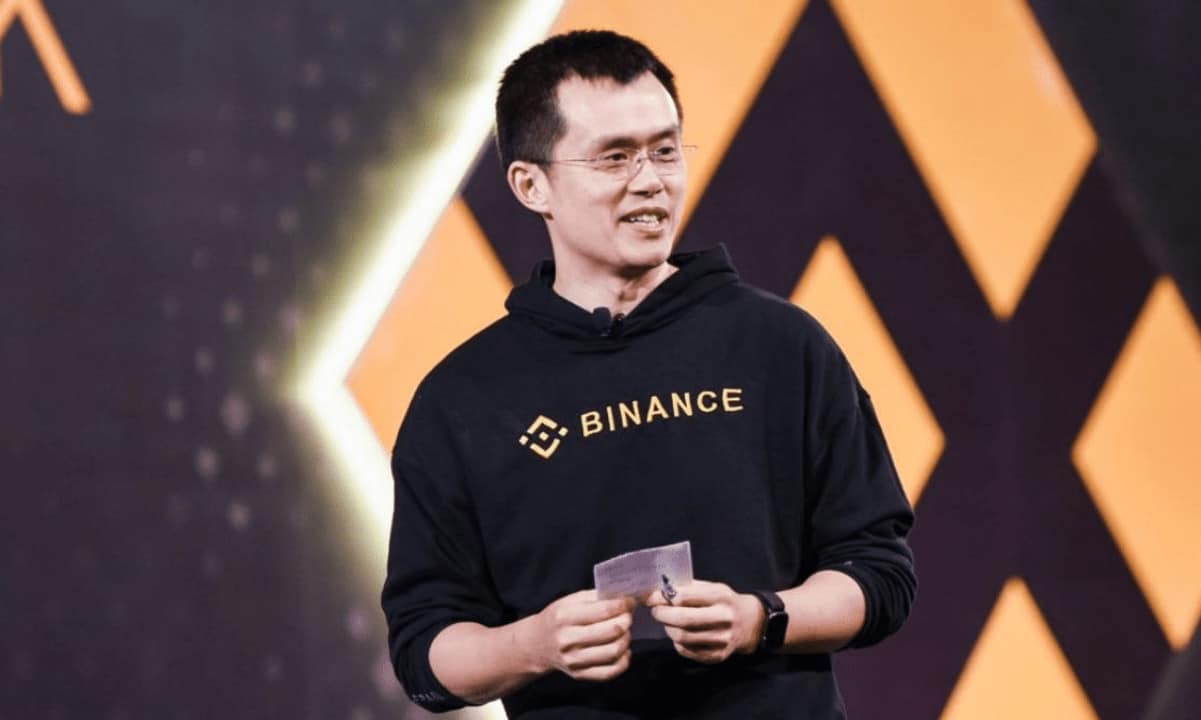 Image: CryptoPotato
Two PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, were patched on October 21, 2026. They carry a severity score of 9.2 and allow unauthenticated attacks. BitGo said its platform was unaffected. Changpeng Zhao warned users to be careful on websites for the next few days. NSA Cyber and the FBI advised organizations to patch or take affected systems offline.
Key points
- The flaws carry a severity score of 9.2.
- Attackers need no login to exploit the vulnerabilities.
- Organizations were advised to patch immediately or take affected systems offline.
Why it matters
The flaws sit in widely used PHP web software and need no login. Zhao warned that visiting a site could lead to stolen credentials or a compromised device. BitGo said its platform was unaffected.
What's unclear
One account says no functional exploits were found when the patches were released, while another says exploitation was confirmed in the wild soon after disclosure.
Sources · 2 publishers
CryptoPotato
Tier 2
CZ Warns Crypto Users as Critical PHP Vulnerabilities Put Websites at Risk
Coverage timeline
- First reported by Crypto Briefing
- Also reported by CryptoPotato
- CryptoVideos brief published
How this page is checked. AI drafted this brief from selected independent reports. Automated checks compare numbers, source coverage and topic terms, but may miss errors. Publication and evidence refreshes run automatically. Read the linked reports for context. Report an error